
DAST
Find and fix exploitable runtime vulnerabilities
Simulate real-world attacks on web applications and APIs so you can understand your true exposure and rapidly remediate risk.




Application security coverage from code to runtime
Prioritize exploitable runtime vulnerabilities
DAST takes a “black box” testing approach, simulating attacks on a running application to identify vulnerabilities and misconfigurations.
Each scan attempts safe, read-only exploits, so you have visibility into exploitable runtime findings and can accurately prioritize and remediate these risks.

Uncover security blindspots
Accurately map entry points in your running applications and discover unknown assets, including those that have been abandoned, forgotten, or created unofficially, giving you visibility into your true security risk and exposure.

Connect code to runtime risk and fix what’s truly exploitable
Remediate faster by correlating SAST and DAST findings. Mend SAST flags vulnerabilities with confirmed runtime exploitability—matching issues by CWE, URL, and API endpoint—so you can focus on real risks, not false positives.

Automate dynamic scans in test and production
Find vulnerabilities, verify their accuracy, and route issues to developers without manual intervention. By automating these three steps, you can save your teams hundreds of hours each month.

Everything you need to secure what you ship
Built for every team
AI security, application security, and dependency management — less tool sprawl, more risk reduction.

Mend AI


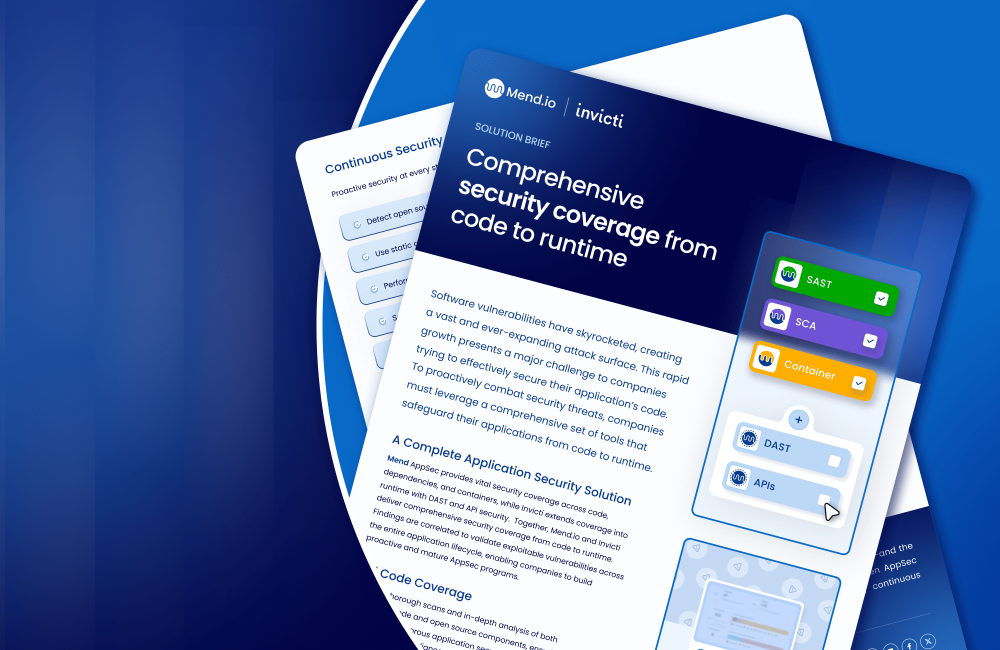
See how Mend.io and Invicti extend your AppSec coverage from code to runtime
Mend AppSec provides vital security coverage across code, dependencies, and containers, while Invicti extends coverage into runtime with DAST and API security.
Learn more about how we can help

Simulate real-world attacks on your AI applications before deployment

Find exploitable threats before pushing them to production

Scan container images and K8s to identify and address risks ahead of deployment
Trusted by security teams all over the world


If we look at the number of PRs created by Mend SCA that were merged and compare that to the cost of developers doing that manually, then we have saved considerable developer time.


One of our most indicative KPIs is the amount of time for us to remediate vulnerabilities and also the amount of time developers spend fixing vulnerabilities in our code base, which has reduced significantly. We’re talking about at least 80% reduction in time.


When the product you sell is an application you develop, your teams need to be fast, secure and compliant. These three factors often work in opposite directions. Mend provides the opportunity to align these often competing factors, providing Vonage with an advantage in a very competitive marketplace.


The biggest value we get out of Mend is the fast feedback loop, which enables our developers to respond rapidly to any vulnerability or license issues. When a vulnerability or a license is disregarded or blocked, and there is a policy violation, they get the feedback directly.
FAQs
How does Mend.io test running applications?
Mend AppSec pairs with DAST and API Security from Invicti to simulate real-world attacks against running applications, automating DAST, API, and container security scans across your development lifecycle.
How does dynamic testing extend Mend.io’s pre-production coverage?
Pre-production scanning covers risks in code; dynamic testing validates what the application actually does at runtime, surfacing reachable, exploitable risks from code to cloud.
How does DAST eliminate false positives in dynamic testing?
Proof-based scanning safely exploits each vulnerability to confirm it’s real, so teams only work on verified, exploitable risks.
Can API Security find APIs I don’t know about?
Yes. It discovers and inventories applications and APIs, including those that are lost, undocumented, or unauthorized, closing gaps attackers look for first.

Stop managing alerts.
Start reducing risk.
Join the teams reducing remediation effort by 75%.